Select another country or region to get content for your location.

Miercom — independent product security testing across the MAXHUB Teams Rooms range

Question we hear most often: "On Teams Rooms the operating system and the Teams application are secured by Microsoft, and we already have Microsoft's security documentation for those. But the hardware is yours, and so is the software layer you add on top of it. Has anyone independently tested the part MAXHUB is responsible for?"

Short answer: yes. Miercom, an independent US-based product test laboratory, has conducted security testing across four MAXHUB Microsoft Teams Rooms products — covering the hardware, the device firmware, and the MAXHUB-supplied software running on it, on both the Windows and Android platforms.

What MAXHUB is responsible for, and what Microsoft is

On a Microsoft Teams Rooms device, the security model is shared. Microsoft supplies and secures the operating system — Windows 11 IoT Enterprise, or the Android-based Microsoft Device Ecosystem Platform — and the Teams Rooms application itself. MAXHUB supplies the hardware, the platform and device firmware, and the MAXHUB software components that run alongside Teams.

The Miercom engagement exists to provide the independent evidence for the layers MAXHUB owns, so that a security review can cover the whole device rather than only Microsoft part of it.

Why Miercom specifically

Miercom is an independent product testing laboratory that has operated for over 30 years, conducting security and performance testing for networking, communications and collaboration vendors. The engagement was scoped for breadth across the product range, so that a customer deploying a mixed estate has independent testing covering each device type they are buying. It complements our IOActive engagement, which assessed MAXHUB OS — the MAXHUB-developed environment on our interactive flat panels — in depth with privileged access.

Products assessed

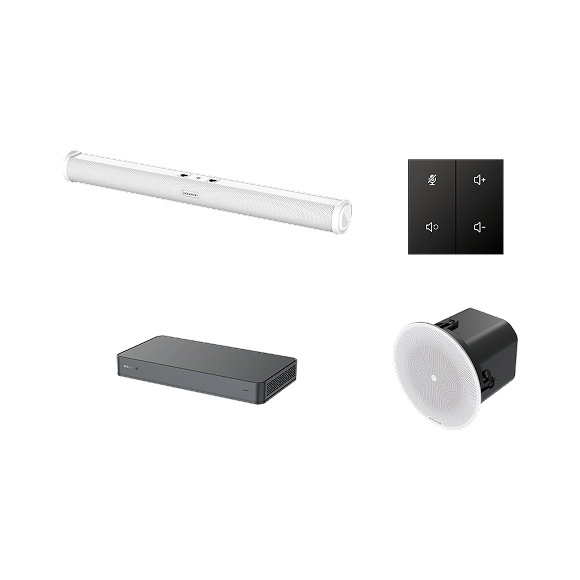
  • MAXHUB XBar V50 Kit — Android platform (Microsoft Device Ecosystem Platform)
  • MAXHUB XBar W70 Kit — Windows platform
  • MAXHUB XBoard V7 in Microsoft Teams Rooms configuration
  • MAXHUB XCore Kit Pro compute module

What was tested

  • Network service exposure — enumeration of open ports, listening services, and the protocols in use on each device.
  • Protocol security — identification of insecure or plaintext services reachable over the network.
  • Known vulnerability review — assessment against public CVE sources and CISA advisories applicable to the platform and its third-party components.
  • Administrative access controls — the availability and protection of privileged interfaces and the ability to install software on the device.
  • External communications — identification of the external destinations each device contacts during normal operation and during software update checks.
  • Security documentation and disclosure — availability of published security guidance and vulnerability advisory information for the products.

Findings

The assessment documented the external destinations contacted by the device during operation and during update checks. Miercom's published destination table records no endpoints in China.

On findings and scope

The Miercom reports record both PASS and MARGINAL ratings, and the full reports are available so that customers can see the findings and our responses rather than a summary. This engagement assessed the devices as they present to the network. Platform-level protections, secure boot, TPM and hardware attestation, drive encryption, and physical interface security, are documented in the per-product security whitepapers, and MAXHUB OS was separately assessed in depth by IOActive.

How to obtain the reports

The Miercom reports are available to qualifying customers and prospects. Request them via the document library.

{$ text $}

{$ title $}
pic